




AI SECURITY & GUARDRAILS
Every package, model and agent is secured and governed before it ships, and stays governed once it’s running.
Every new model, package and integration expands your attack surface, and most security teams can’t see what’s actually running in production. Agentic AI makes it worse when agents pick their own dependencies and tools.
in the wild, available to developers with no security guardrails.
found over 2 months across 25K MCP servers, affecting 73% of them.
will come from compromised models and datasets by 2029.
found across 2M+ publicly available AI models.
Every unvetted package, model and agent creates exposure, whether you see it or not. Incident response, breach disclosure and compliance findings all cost more than the secure foundation and validation that would have caught it first.
For more than a decade, Anaconda has helped enterprises build on trusted Python and open source. Today, that trust extends across packages, models, agents and MCPs across the full AI-native development lifecycle from experimentation to production.
new to anaconda
AI development is getting more agentic. Enkrypt AI brings security validation and guardrails right into your workflow running inside your own environment and tools of your choice.
Every package, model and agent follows a governed path through pre-deployment validation, runtime protection and continuous compliance. Anaconda’s trusted open-source foundation combines with Enkrypt AI’s agent security capabilities to extend trust from development through production.
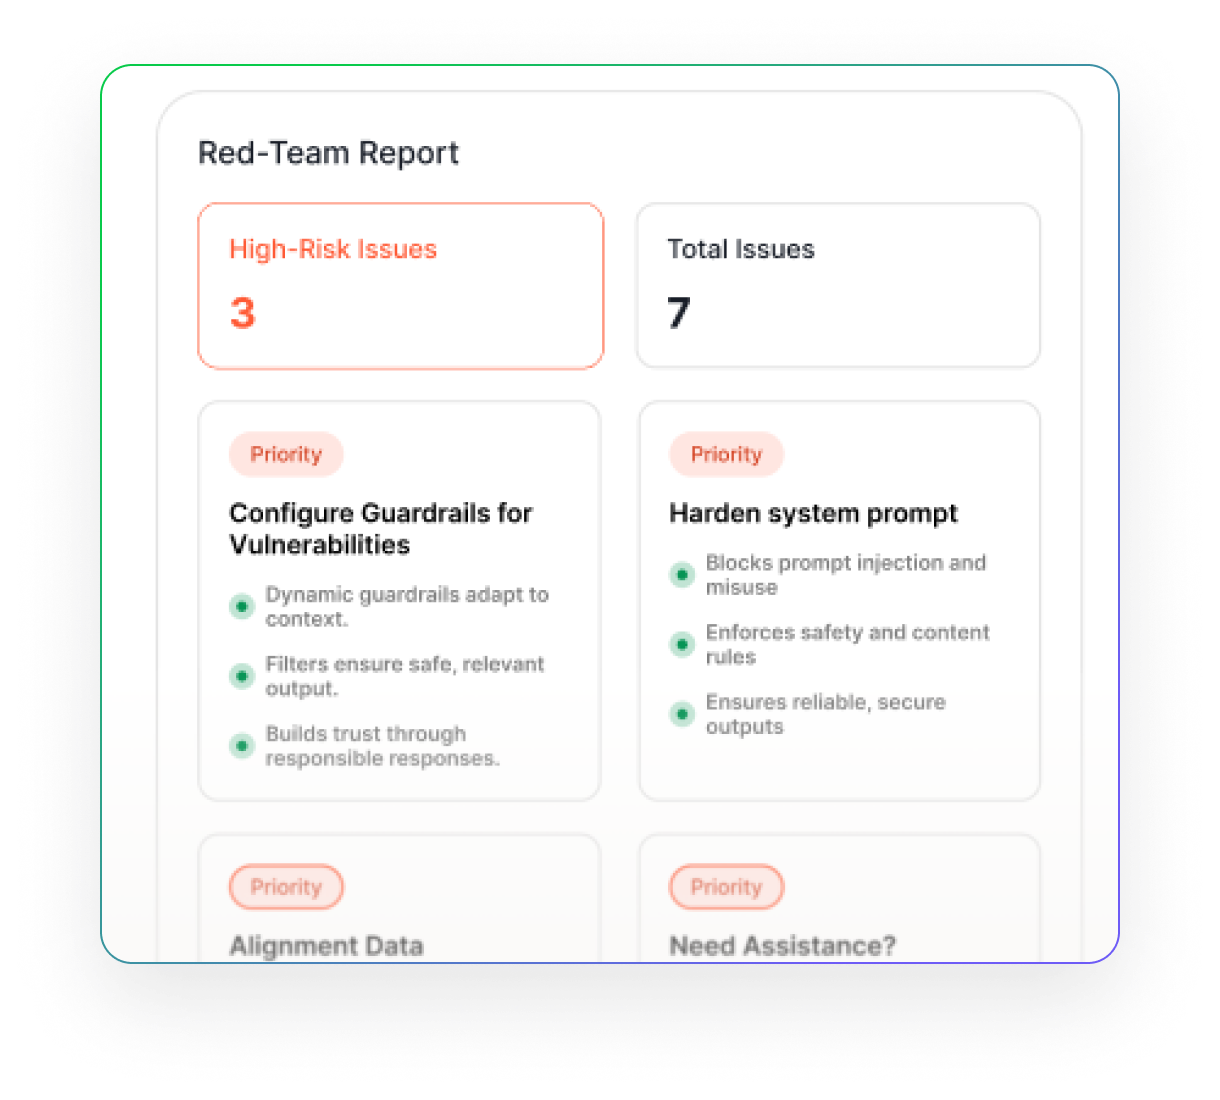
Automated adversarial security testing of AI models and agents before they ship and continuous evaluation after deployment.
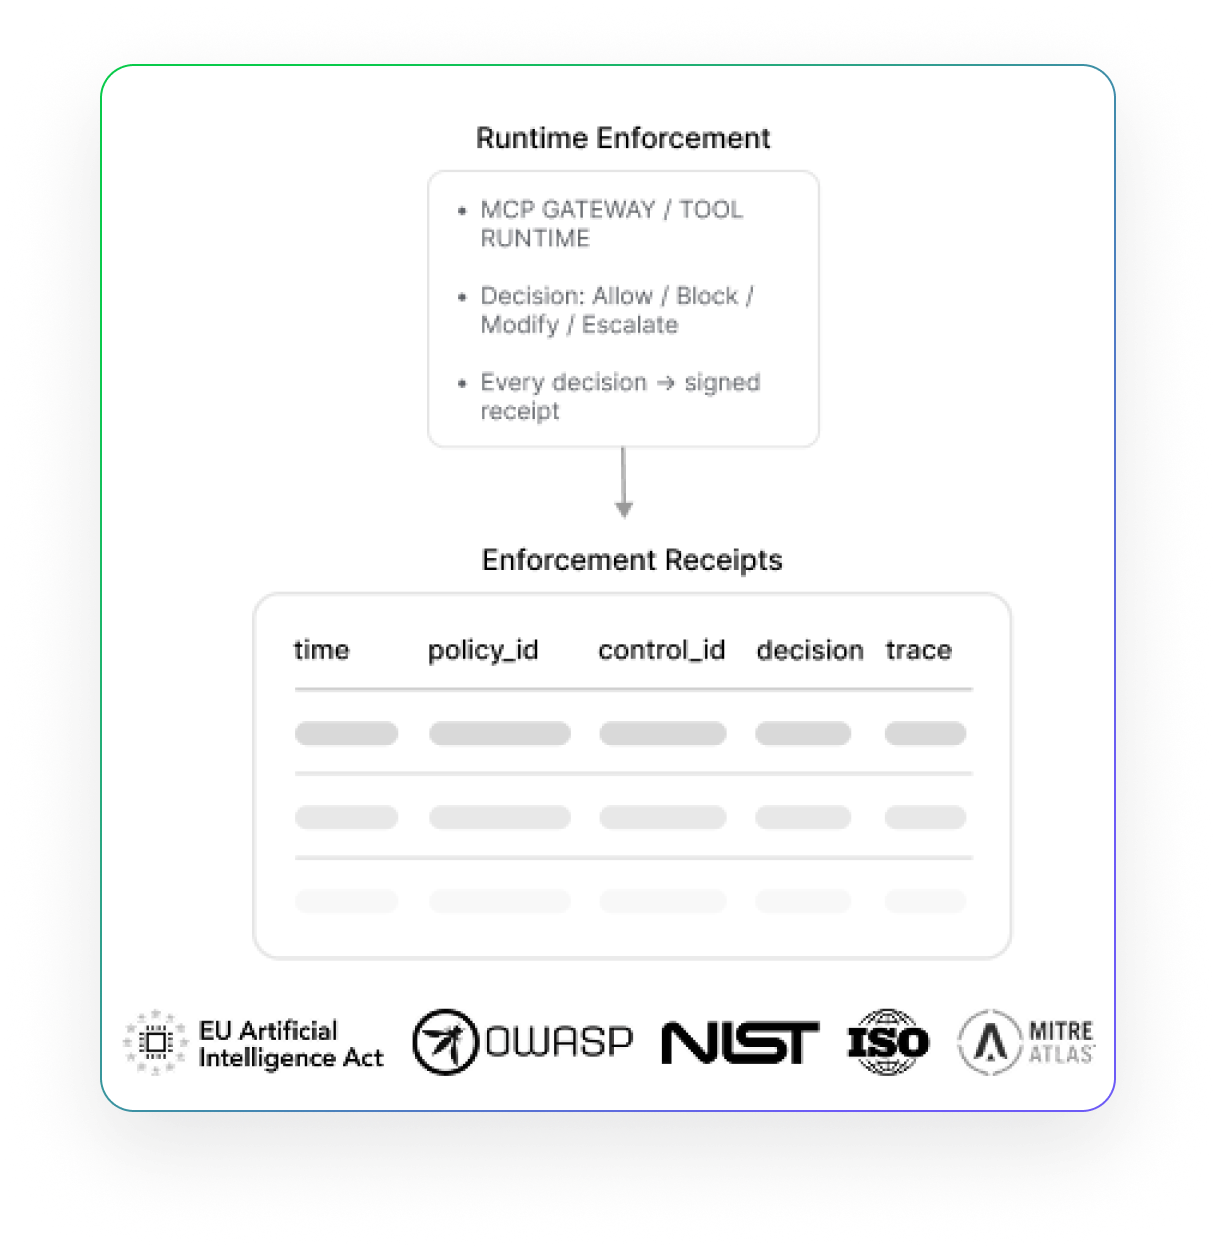
Runtime guardrails constrain agent behavior in real time.
Continuous evidence collection for AI regulatory frameworks, not a periodic audit.
Security validation, guardrails and policy enforcement run inside your environment across clouds, frameworks and models. Compliance becomes an everyday operating control, not a once-a-year audit exercise.
BEFORE & AFTER
Continuous vulnerability scanning and usage observability
Discover unsafe agent behavior after an incident
Red-team models and agents before they ship
Hope agents stay in scope
Runtime guardrails constrain behavior in real time
MCP governance bounds and audits every connection
Compliance is a once-a-year scramble
Compliance evidence collected automatically, continuously
Trust routed through an external provider’s promises
Validation runs inside your own environment
Security is a gate at the end of the workflow
Security is built into every step
Enforce security and compliance without becoming the bottleneck. Automated evidence maps EU AI Act and NIST AI RMF requirements to continuous controls.
Enable innovation without another stack to manage. Give teams consistency, keep developer choice.
Ship agents without waiting for manual security reviews. Guardrails operate automatically in the environment where you already build and run.
The attack surface keeps expanding while the security and compliance bar continues to rise. New models, connections and regulatory requirements should strengthen existing controls, not create another governance process.
Get the validation, guardrails, monitoring and compliance evidence you need to secure packages, models and agents from development through production. Give builders the freedom to move fast without losing control.
how it works
Complete the form, and we’ll reach out within 1 business day to discuss your requirements. Then, we’ll build a demo that addresses your real challenges.
AI security & guardrails provides continuous assurance across the Anaconda Platform: Build in AI workspaces, validate and protect before and after deployment, then scale with AI orchestration.
Packages, models, and agentic development environments to build with.
Get more AI ideas out of experimentation and into production, faster.
Start from trusted open-source building blocks, secured and governed for enterprise use.